 近期通过邮件系统 IMAP 从外部、POP3 和 SMTP 等开放端口在尝试内部账户邮箱密码的情况越来越频繁,虽然邮件系统有一定的机制可以阻挡,But seeing so many IPs in the report is really uncomfortable,So I started collecting these IPs intending to import them all into the Sonicwall firewall,Directly set them as a blacklist,After searching online for many articles,Sonicwall does not provide a relevant way to do this,Therefore, if you want to create these massive IPs into Address Objects,Using SSH would be the most time-saving method。
##########################

# Sonicwall

# 型號:NSA 4600

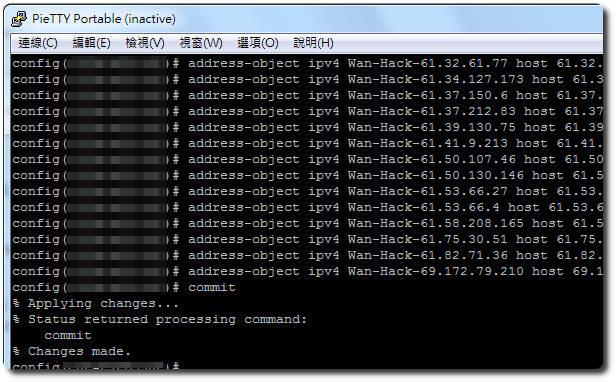
# 韌體:6.2.7.1

# SSH 工具:PieTTY 或 Tera Term

##########################
1. 首先透過 excel 和 wxMEdit 將 IP 整理成如下格式:
address-object ipv4 Wan-Hack-1.1.1.1 host 1.1.1.1 zone WAN
address-object ipv4 Wan-Hack-2.2.2.2 host 2.2.2.2 zone WAN

# 其中 Wan-Hack-1.1.1.1 欄位,可以透過 Excel 函式去抓後面的欄位
# 如 ="Wan-Hack-"&LEFT(E1,15)
# E1 為 1.1.1.1 所在的欄位。
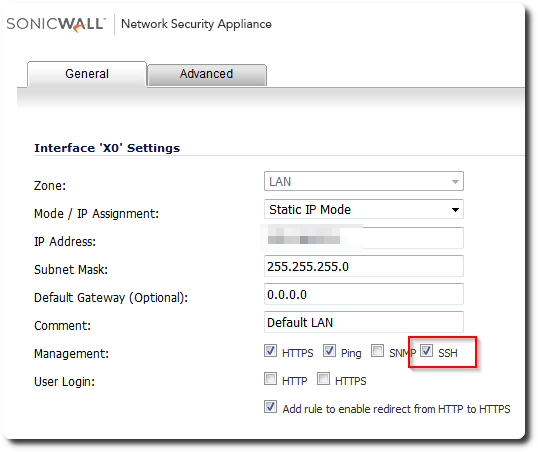
2. 再來透過 PieTTY 或 Tera Term 連上 Sonicwall ,如果先前沒有打開 SSH 連線,可以到 Network 底下的 Interface 去設定開啟。
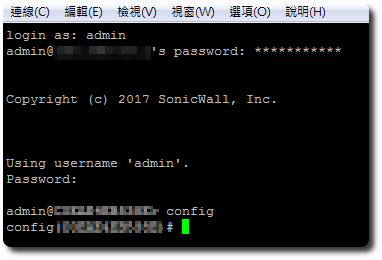
3. 登录后,Enter”config”進入設定模式。
4. 接著將整理好格式的 IP 清單,貼到 PieTTY,這邊要注意一下,如果整理的清單有上千筆,建議分批貼上,一次最多不要超過 400 筆,每貼上 400 筆就執行”commit”存檔,再進行下一個 400 筆,依此類推,如果一次貼 500 筆以上,可能會出現錯誤的情形。
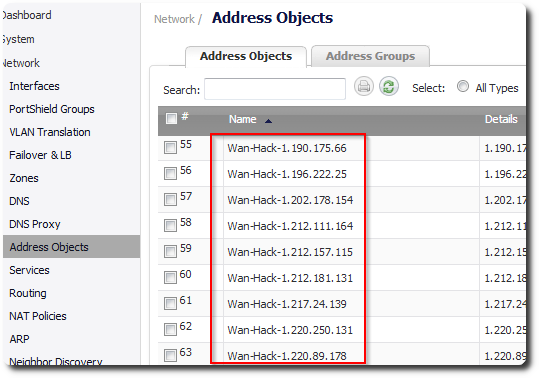
5. 完成之後,就可以在 Address Objects 看到刚刚导入的 IP 地址。
【参考资料】
- 在命令行界面中创建对象和组 (CLI) 用于 5.8 以下 | SonicWall
- Sonicwall 脚本生成器 – 创建多个地址对象并将它们添加到地址组 | Phy2Vir


留下回复